Alert Advisory: Customer Advice Regarding the AnyDesk Incident
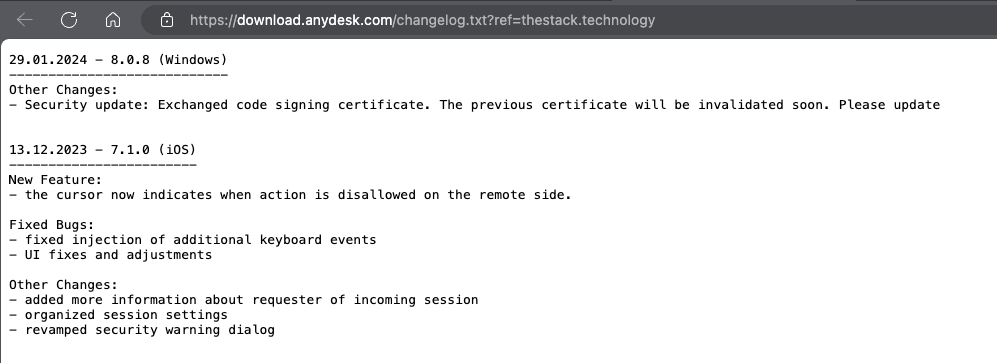
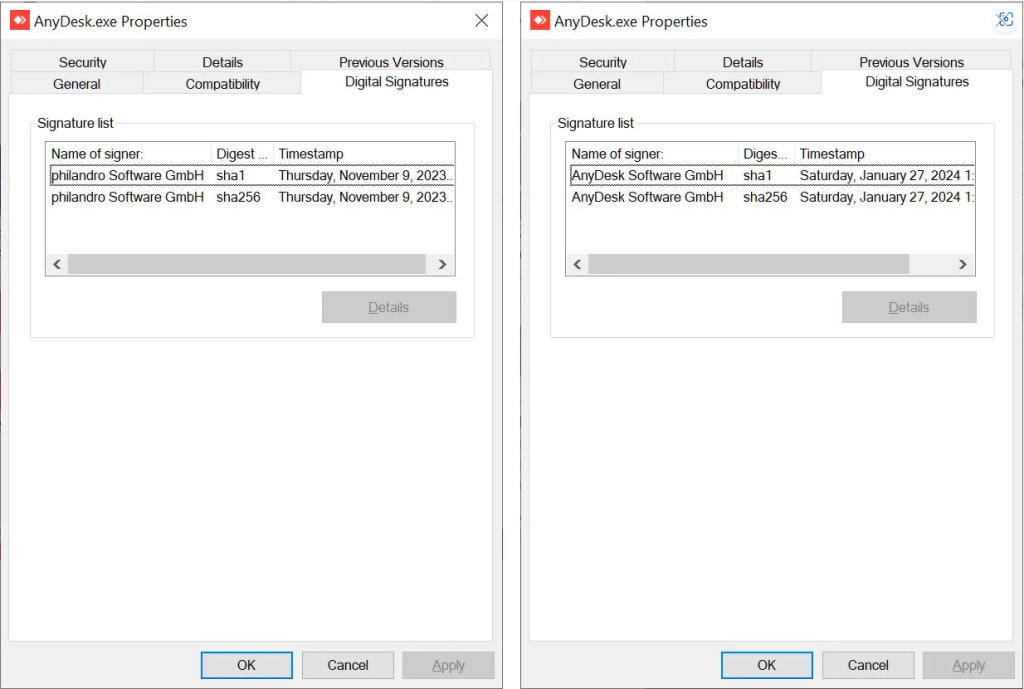
The following query can be used to locate executables in an environment that were signed with the previous, to-be-revoked certificate (including prior versions of the Anydesk client):
DeviceFileCertificateInfo
| where TimeGenerated >= ago(31d)
| where CertificateSerialNumber == “0dbf152deaf0b981a8a938d53f769db8”
and Signer == “philandro Software GmbH”
| project TimeGenerated, DeviceName, CertificateSerialNumber, Signed
It is strongly suggested that all users install the most recent version of the software (version 8.0.8 for Windows; other binaries continue to utilize the old certificate), as the old code signing certificate will be revoked soon. Anydesk has initiated a mandatory password reset for their customer portal, my.anydesk.com, and has advised users to update their passwords. Users are urged to also change any identical passwords used on other portals.
An Iranian threat group called OilRig typically targets businesses in the Middle East involved in various industries. Still, it has […]
This week’s cybersecurity developments highlight the growing sophistication of modern threats and the pressing need for a proactive, multi-layered defense […]
Cisco recently resolved a significant security vulnerability in the Unity Connection. Unity Connection is a fully virtualized messaging and voicemail […]